Save Your SSH Connections,
Run AI Agents on the Remote Box
AgentsRoom is an SSH connection manager and a built-in SSH terminal in one. Save your remote servers once, connect with an SSH key or a password, then run Claude Code, Codex or Antigravity CLI straight on the remote machine.
Stop juggling a separate SSH client and a code editor. Keep your connection profiles, your terminal and your AI coding agents in the same app, pointed at the same remote server.
How AgentsRoom connects to a saved SSH server and runs an AI coding agent straight on the remote machine.
Most AI coding agents assume your code lives on the same machine you are sitting at. But plenty of work happens on a remote server : a VPS, a staging box, a beefy build machine, a shared dev server the whole team uses. AgentsRoom treats that case as a first-class one. Save an SSH connection, open the built-in terminal over SSH, and you are working on the remote host as if it were local.
The SSH connection manager keeps a profile for every server you touch : host, port, user, and whether you authenticate with an SSH key or a password. No more digging through scattered config files or retyping the same long command. Pick a saved connection, hit connect, and the terminal lands you on the box in one step.
The payoff is running AI coding agents where the code actually is. Connect to your remote server over SSH, then launch Claude Code, Codex, Antigravity CLI or another agent on that machine. The agent reads and edits the files on the remote host, runs the test suite against the remote environment, and you drive the whole thing from AgentsRoom without a second SSH client open on the side.
An SSH Client Built for Running AI Agents
Connection management, a real terminal, and remote agent execution in one place.
Saved SSH Connections
Store a reusable profile for each remote server : host, port, user and auth method. Your VPS, your staging box and your team dev server all live in one list. Pick a connection and you are in, no command to retype.
Key or Password Auth
Authenticate with an SSH key or a password, whichever the server expects. Point a profile at your private key file or store a password, and AgentsRoom handles the handshake when you connect.
Built-in Terminal Over SSH
Every connection opens a real terminal on the remote host inside AgentsRoom. Full colored output, command history and copy-paste, served by the same terminal you already use for local projects. No separate SSH client to keep open.
Run Agents on the Remote Server
Launch Claude Code, Codex, Antigravity CLI or another agent directly on the remote machine over SSH. The agent works on the files that live on the server and runs commands in the remote environment, not on your laptop.
Attach SSH to a Project
Flag a project as remote and bind it to a saved SSH connection. From then on the project opens its terminals and agents on that server, so a remote codebase behaves like a normal AgentsRoom project.
Credentials Stay Out of the Repo
Your SSH keys stay on your machine and passwords stay encrypted in its keychain, unless you turn on synced passwords, which carry them end-to-end encrypted. Nothing is ever written into the project repo, so nothing about your servers leaks into a folder a teammate might clone.
Import Your ~/.ssh/config
The servers you already reach from a terminal come in as they are. AgentsRoom reads the host blocks in ~/.ssh/config, keeps the identity file each one declares, and preserves a ProxyJump through a bastion : it connects through the alias and lets OpenSSH resolve the block, exactly as your shell would.
AWS SSM Sessions
Reach an instance that has no public address and no inbound SSH port, through aws ssm start-session. The session is authorized by the AWS profile already configured on your machine, so there is no password and no key to store in the app.
WinRM and PowerShell Remoting
Reach a Windows host that has no OpenSSH but speaks WinRM, with NTLM for a workgroup machine or Kerberos for a domain member, including the PowerShell endpoint of an on-prem Exchange. CredSSP covers the second hop, when the session must in turn reach Active Directory or a file server: HTTPS with a checked certificate, and the form warns you that the password is handed to that server. From a workstation outside the domain you name the domain controller and the server IP yourself, and AgentsRoom handles the lookups without touching your hosts file. Agents run PowerShell through it read-only by default; writes wait for your confirmation, every one of them, only the risky ones, or none, as you choose per connection.
Your Passwords Stay Encrypted, on Your Machine by Default
An SSH connection manager is only useful if you can trust it with credentials. The name, host, port and user of a connection follow your account, so a server saved on one computer appears on the others without being retyped. Your SSH keys stay on the machine, and passwords and key passphrases stay encrypted in the keychain of the machine where you typed them. Turn on synced passwords in Settings > Account (off by default) and they follow too, end-to-end encrypted with a key only your computers hold: AgentsRoom stores them without being able to read them. Nothing is ever written into the project you are working on: connecting to a remote server never adds a config file to the repo and never commits a host or a secret by accident.
Authentication runs over standard SSH. Key-based login uses your existing private key, exactly as your shell would. Password login is sent over the encrypted SSH channel like any other SSH client. AgentsRoom is the client, your server stays the source of truth for what it accepts.
When you run an AI agent on the remote box, the code stays on the remote box. The agent reads and edits files on the server you connected to. Nothing about the remote project is copied to your laptop unless you ask for it, and your connection profiles are never shared with anyone else.
From Zero to Agent on a Remote Server
Save a connection once, run agents on it forever.
Save the SSH connection
In a project, click Servers in the dev command bar, then Add a connection, or Import from ~/.ssh/config to bring in the hosts you already have. A profile holds the host, port, user, and either your SSH key file or a password. Give it a name like prod-vps or staging and it is saved for next time.
Connect and open the terminal
Pick the saved connection and hit connect. AgentsRoom opens a built-in terminal over SSH on the remote host. You are now on the server, with full colored output and command history.
Run an AI agent on the box
Launch Claude Code, Codex or Antigravity CLI in that remote terminal. The agent works on the files on the server and runs against the remote environment, and you drive it from AgentsRoom like any other project.
When You Need Agents on a Remote Server
Not every codebase lives on your laptop.
Code on a VPS
Your app runs on a VPS and you want to fix it where it lives. Open the saved SSH connection, run a Claude Code agent on the box, and patch the bug against the real environment, dependencies and all.
Work on a staging box
A staging server reproduces a bug your laptop never will. SSH in, point a Codex agent at the staging codebase, and let it reproduce and fix the issue on the machine that actually shows it.
Shared dev server
The team works on one shared dev server. Everyone saves the same SSH connection, opens their own terminal, and runs their own agent on the host without setting up a local clone each.
No local setup needed
A heavy toolchain you do not want on your laptop lives on a build machine. Connect over SSH, run a Antigravity CLI agent there, and keep your own machine clean while the work happens remotely.
How can my AI agents access my SSH connections?
Through AgentsRoom MCP. Your saved connections are exposed to every agent as five MCP tools : ssh_list returns the servers usable in the current project (SSH, AWS SSM and WinRM alike), ssh_exec runs one command on a server and hands back its output (a PowerShell line on a WinRM host, read-only unless you allow writes, which you confirm one by one, only when risky, or never, as you choose), ssh_transfer moves one file to or from a server, ssh_connect opens one as a real terminal tab, and ssh_connection_new proposes a server you have not saved yet. So when you tell an agent "connect to prod and read the logs" or "list the Exchange send connectors", it does not have to guess a hostname or write a command by hand : it reads your connection list and works on the right machine.
Agent SSH access is deliberately credential-free. ssh_list only ever returns metadata: name, host, port, user, auth type and scope. Passwords and key passphrases stay encrypted in your OS keychain, private keys stay on your disk, and the desktop app injects the secret into the terminal itself. The agent names a connection, it never handles it.
A session an agent opens with ssh_connect is a visible terminal tab you can read, type into and close at any moment, and a command it runs with ssh_exec comes back in its conversation with its exit code, so you always see what was run and what the machine answered. Files travel the same way : with ssh_transfer an agent pulls a dump or a log off a server, or pushes a file to it, through the same credential-free channel, and gets back a path on your machine rather than the file pasted into its conversation. A connection can be saved for a single project or globally, so an agent only ever sees the servers that make sense for what you are working on. Network appliances whose command line only works inside an open session, such as a WatchGuard firewall or many switches and routers, are covered too: ssh_exec opens the session, waits for the device prompt and types the commands one after the other.
While an agent works on a server, you watch it live. Every command it runs with ssh_exec scrolls in the Activity tab of the right panel, output included, in one journal per server; the agent's avatar shows on the Servers button and, with an Agent at work badge, in your Servers list. A command sent encoded is shown decoded. You can also follow it from your phone, in the agent's card of the mobile app. It only travels between your computer and your phone, end-to-end encrypted with secrets masked: nothing of what runs on your machines is stored on a server.
Creating can also be entirely the agent's job. ssh_connection_new keeps the reviewed path: it opens the creation form pre-filled with what the agent found in a compose file, a deploy script or your documentation, and you are the one who reviews it, types the credential and saves. Unless you turn off "Agents can manage connections" (Settings, on by default), ssh_connection_save writes the connection outright, and even then the credential never travels through the conversation: the agent names a secret from your vault and the desktop copies it. The off switch is written into the setting rather than asked for in a prompt, because a connection an agent could register unseen would be a backdoor.
Discover AgentsRoom MCPFilmed in the app : an agent is asked to check free disk space on a staging server, run a health check script and tail the nginx log. The three calls appear one by one in the Activity tab with their output, their exit code and their duration, then the journal of that server opens in full and leads back to the Servers list. Nothing of what runs there leaves the computer.
Can I save multiple SSH connections?
Does it support SSH key and password authentication?
Can I run Claude Code or Codex on a remote server through SSH?
Where are my SSH credentials stored?
Do I still need a separate SSH client?
Can my AI agents access my SSH connections?
Do my agents see my SSH password?
Can I import my existing ~/.ssh/config?
Can I reach a server with no public address and no open SSH port?
Can an agent create a new SSH connection?
Can I connect to a Windows server and get PowerShell?
Can I open a project that only exists on a remote server, without cloning it here?
Do agents running on a server stop when I close AgentsRoom?
Where do I add an SSH connection in AgentsRoom?
Can the built-in browser open a dev server running on the remote server?
Can I make an agent ask me before it uses a server?
Screenshots
Real captures of the app, added as this feature evolves.
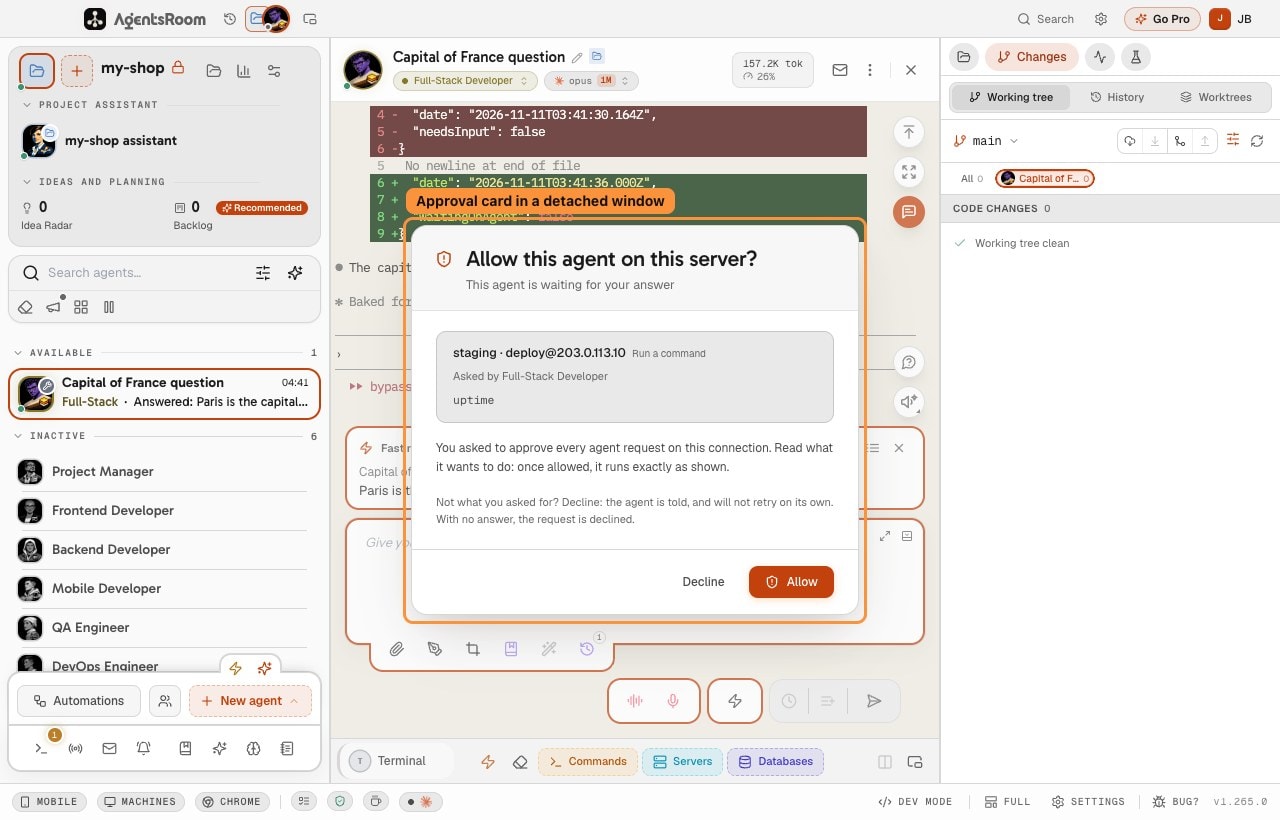
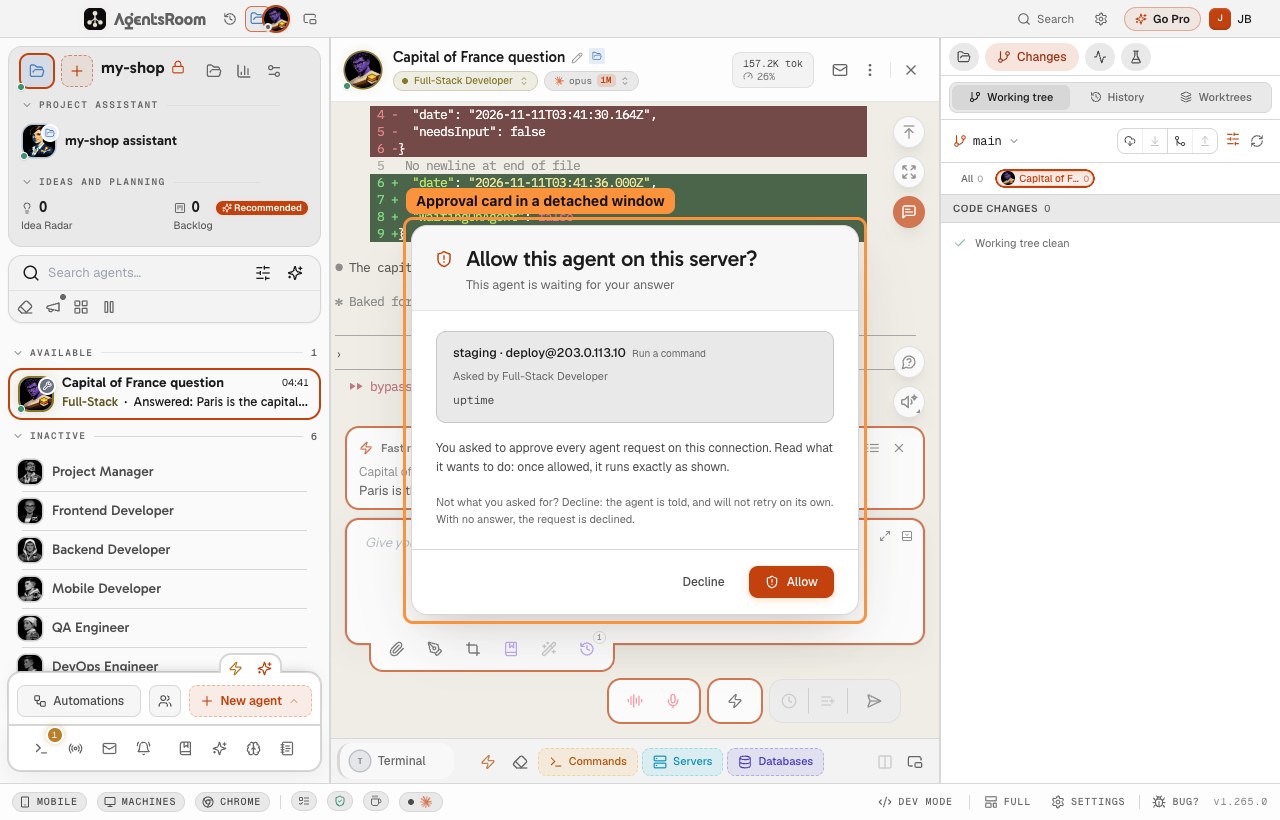
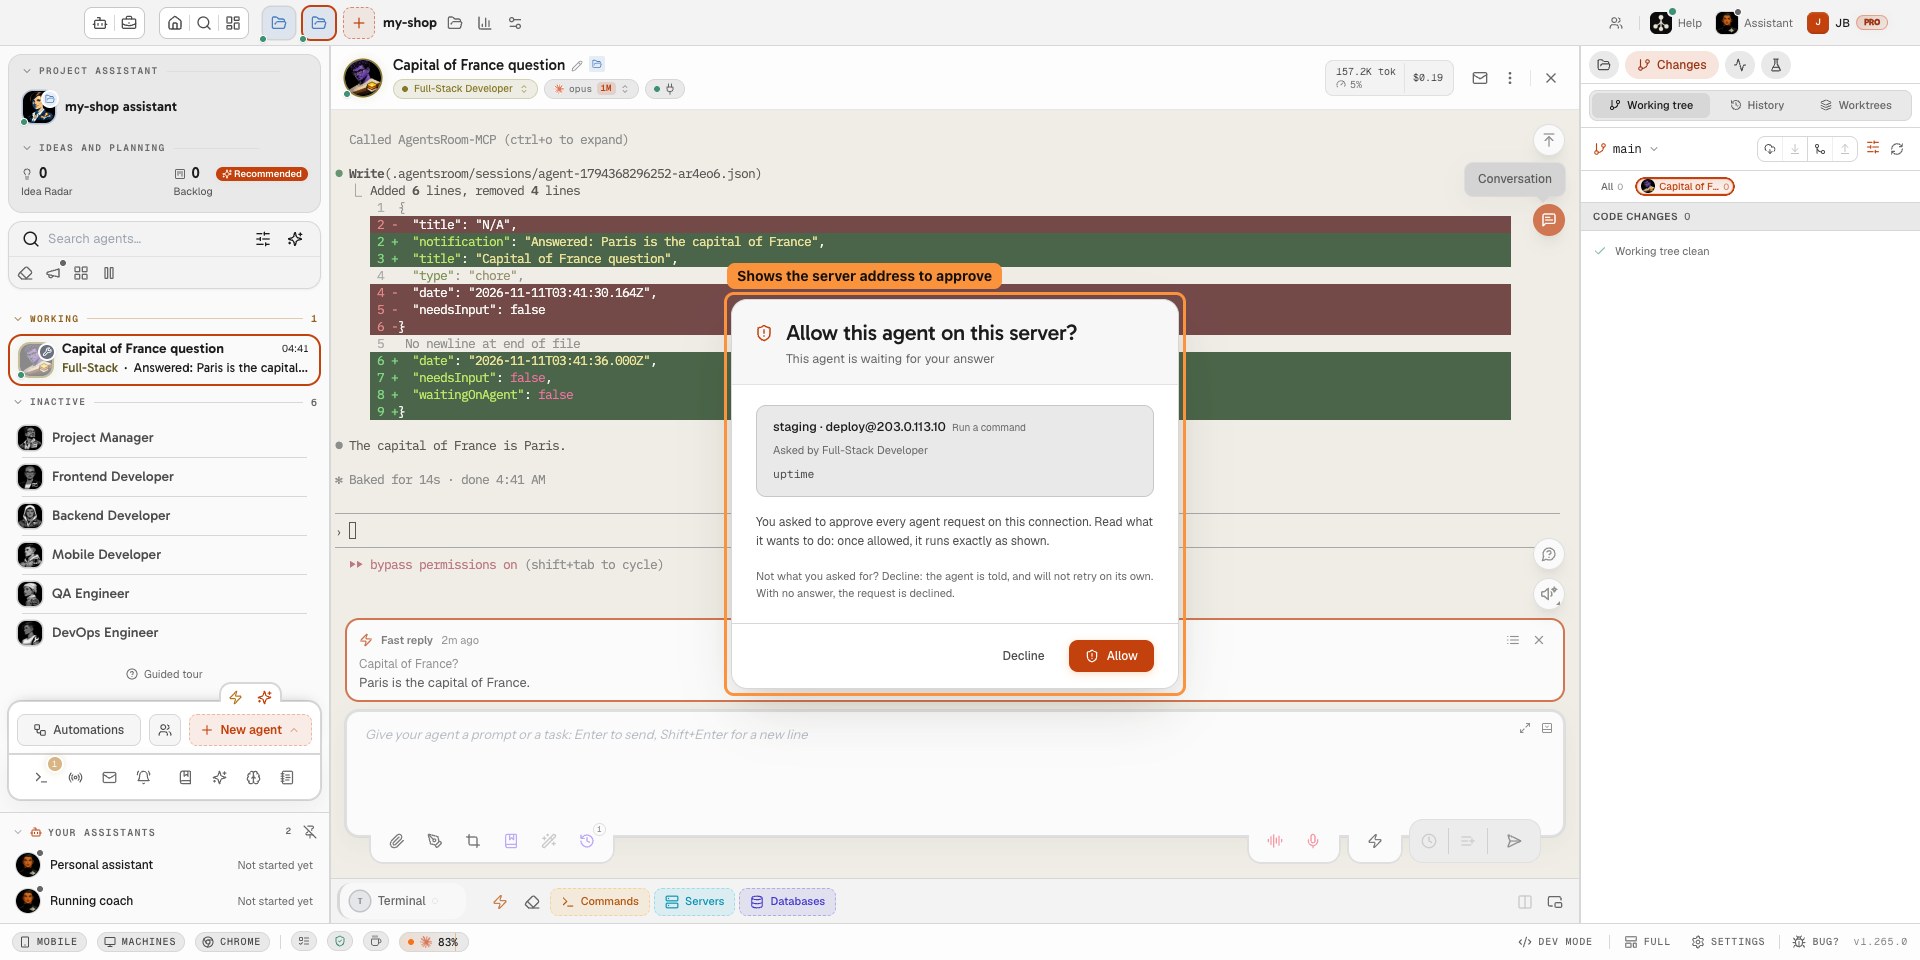
Approve or decline an agent's server command from any project window, even a detached one. 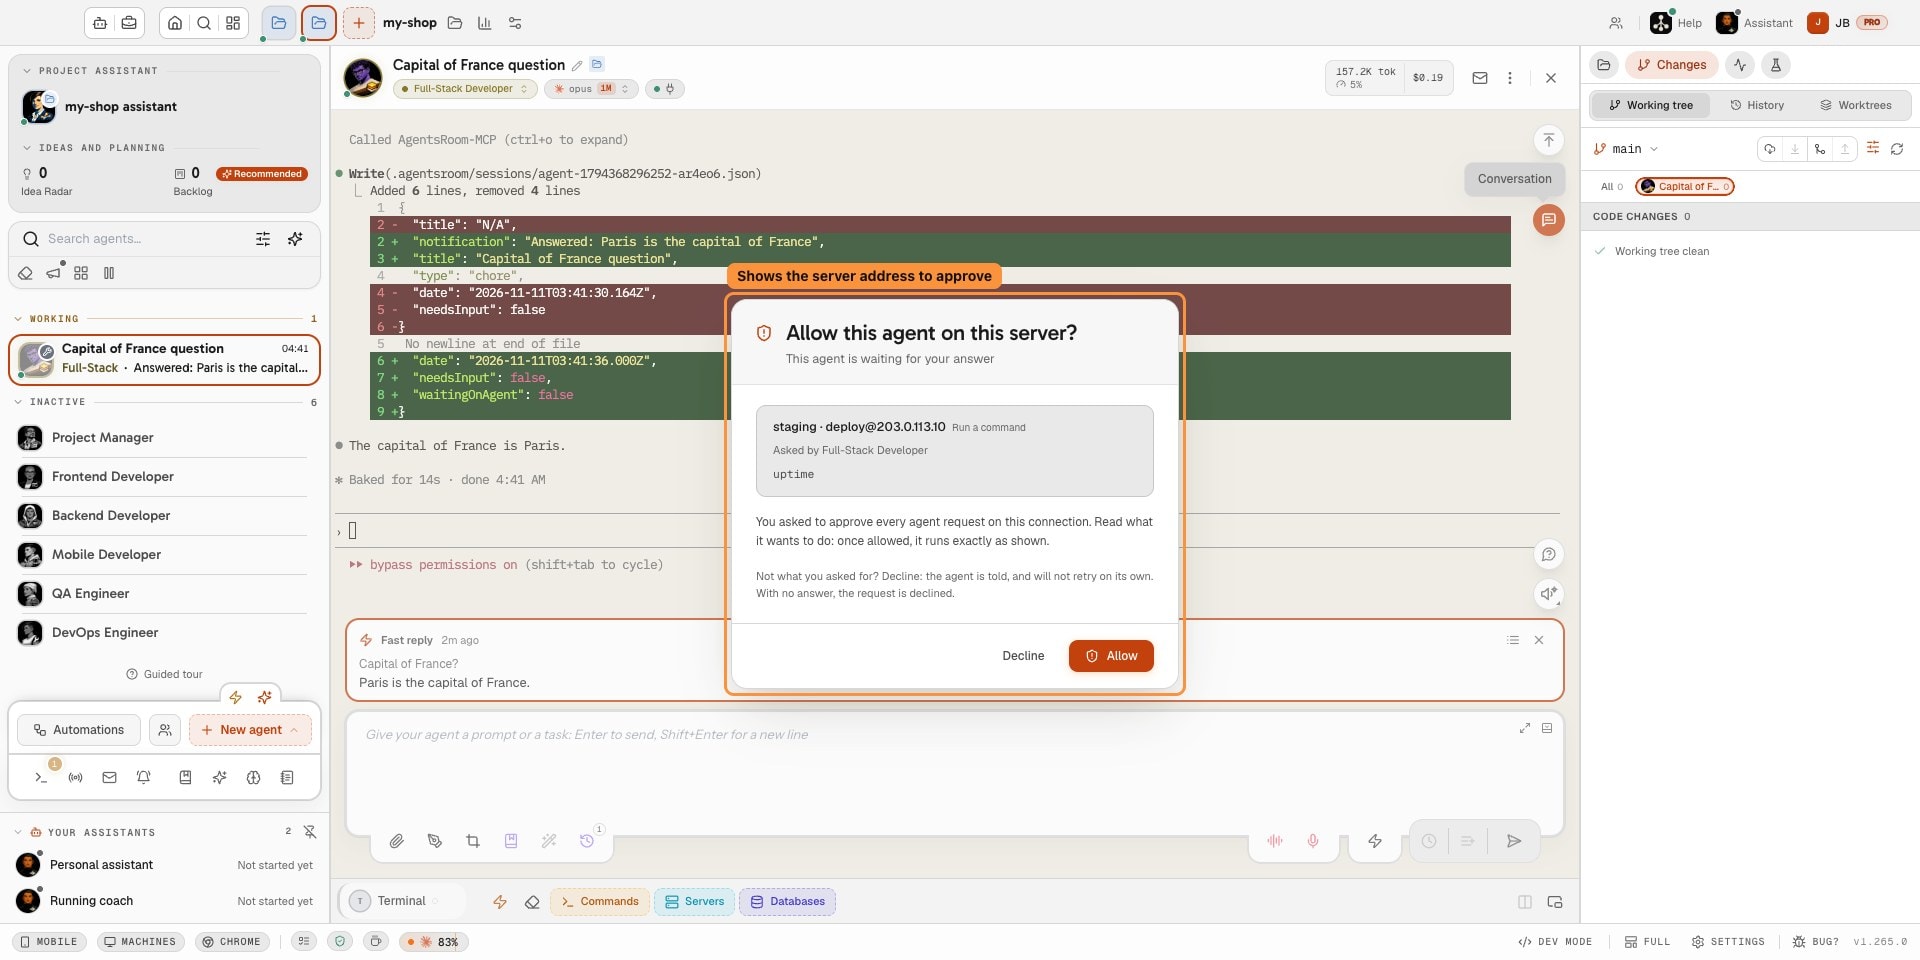
Before an agent runs a command on a protected server, the card shows exactly which server it targets. 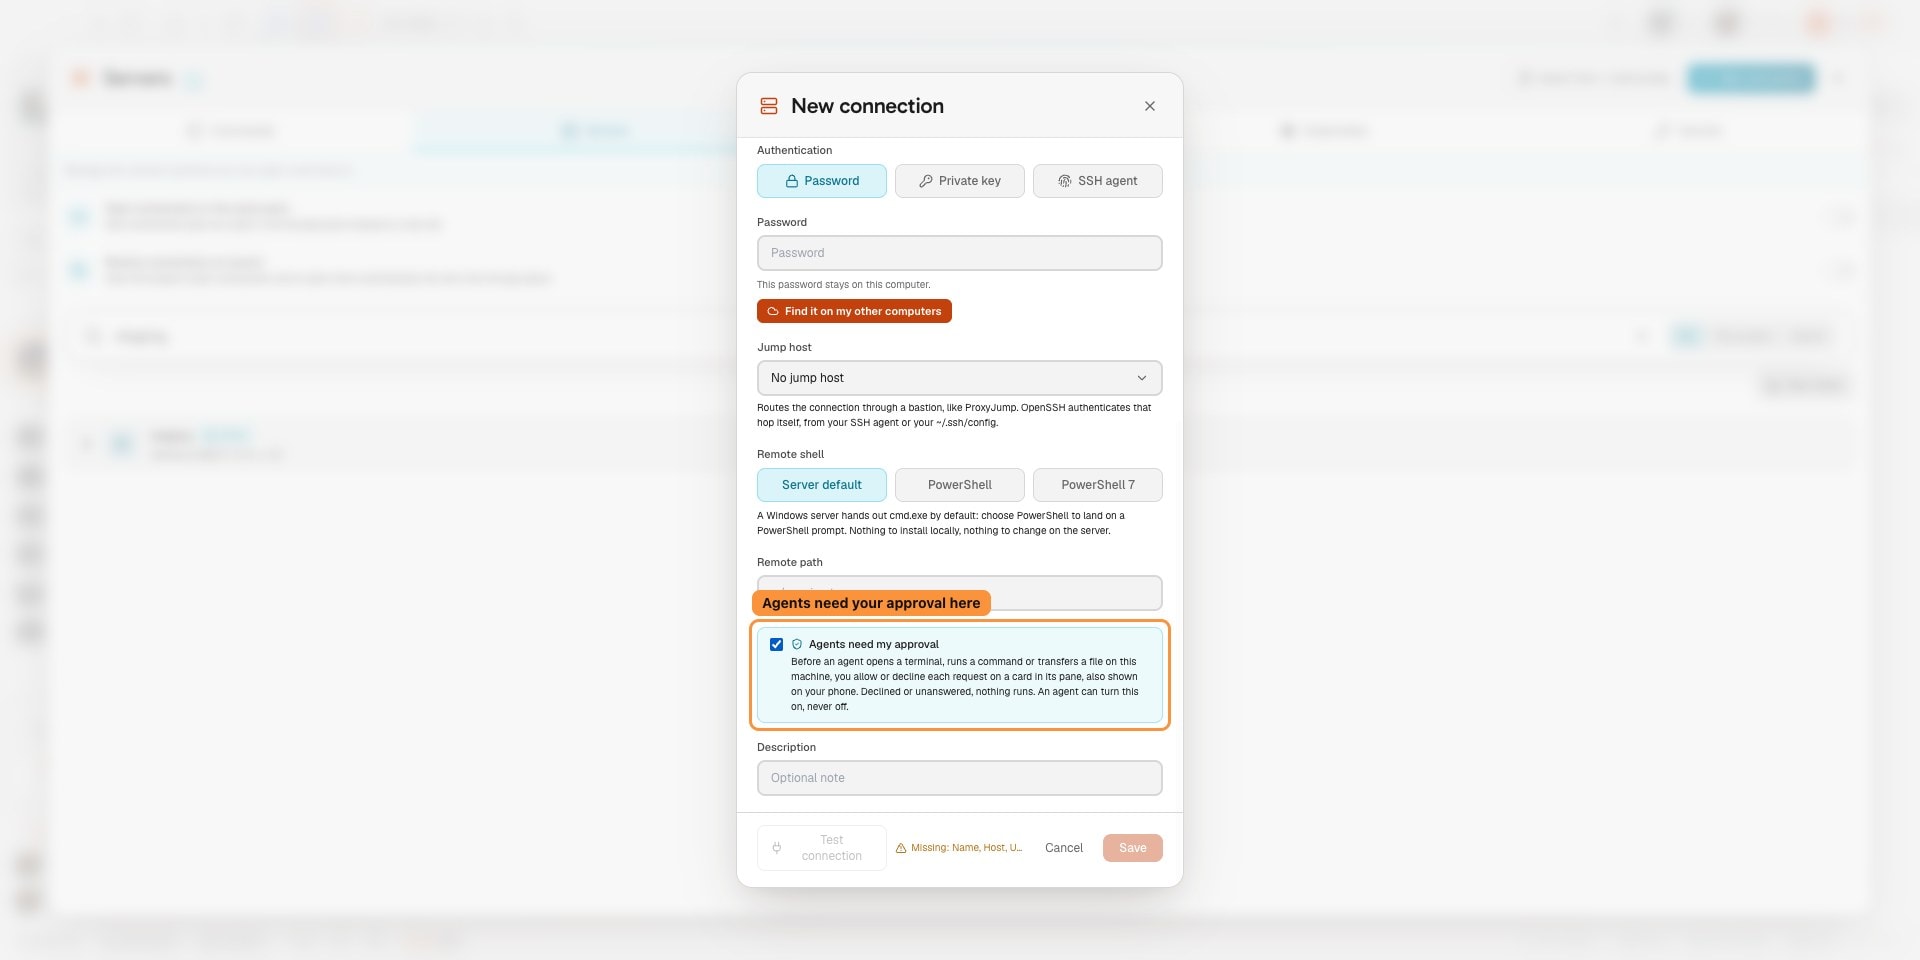
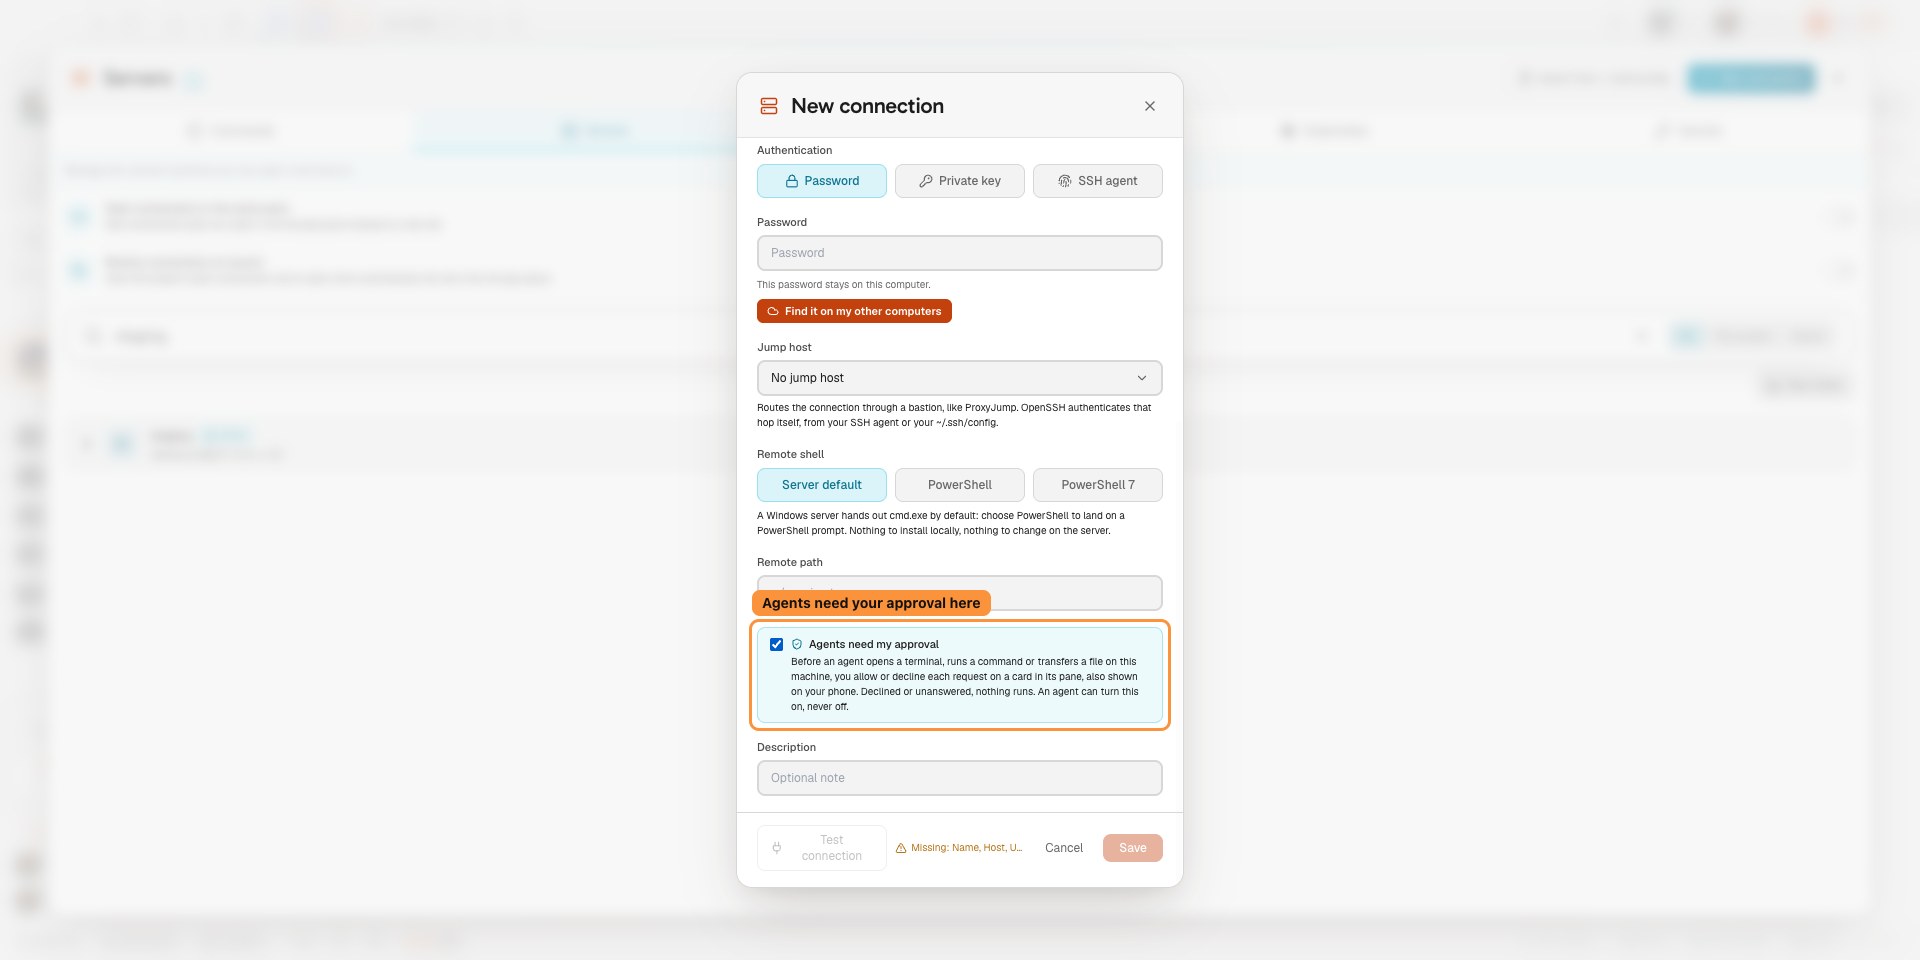
Make agents ask for your approval before they connect to a server, run a command or transfer a file.
You may also like
RDS through AWS SSM
Reach an Amazon RDS instance that has no public endpoint, from your own machine, through aws ssm start-session and the AWS-StartPortForwardingSessionToRemoteHost document. No bastion to maintain, no VPN, no inbound SSH rule. AgentsRoom opens the session on a loopback port and connects its database client through it. MySQL, PostgreSQL, SQL Server and MongoDB, so RDS MySQL, RDS PostgreSQL, RDS for SQL Server, Aurora and DocumentDB.
Database Connections
Save your MySQL, PostgreSQL, SQL Server, MongoDB, SQLite and Google BigQuery connections, reach a database in a private subnet through an SSH tunnel or an AWS SSM session, and let your AI agents query it over MCP. Read-only by default, one statement per call, capped result sets, and the password never reaches the agent. Export, import and database-to-database copy for MySQL, PostgreSQL and MongoDB.
Secret Manager
Store API keys, tokens and passwords in your OS keychain, reference them as {{secret:NAME}} in dev commands and agent environments, and let AgentsRoom resolve them at launch. Agents see the names, never the values, and nothing is ever synced to a server.
Repository import
Connect GitHub or GitLab, browse the repositories you actually have access to, and clone several at once. Each one becomes a project with its own AI coding agents. Self-hosted GitLab instances supported.
Dev Terminals
Per-project terminal manager and process launcher. Start backend, frontend and workers in one click, locally or on a remote server over SSH.
Remote Agent Control
Pilot your AI coding agents from your phone. Drive terminals, projects and prompts on your computer or remote server from iOS and Android.
Localhost Tunnel (Live Preview)
Built-in secure tunnel that exposes a local or remote dev server as a public HTTPS URL. Preview your work in progress from anywhere.
Multi-Project, Multi-Agent
Run many projects and many AI agents in parallel, local and remote, from a single visual command center.
































Bring Your AI Agents to the Remote Server
Download AgentsRoom, save your SSH connections, and run Claude Code, Codex or Antigravity CLI on any VPS or remote server through a built-in terminal.
Companion app: monitor your agents on the go
Bring your own: Claude, Codex, Antigravity CLI, or other AI provider.
Push bugs and requests straight to your public backlog.
Agents you read like a conversation
Each agent has a role, a face, and a thread you read like a messaging app.
