Let Your Agents Query the Database,
Read-Only Until You Say Otherwise
AgentsRoom manages your MySQL, PostgreSQL, SQL Server, MongoDB, SQLite and Google BigQuery connections and gives your AI coding agents a way to run queries against them. Read-only by default, one statement at a time, with the password kept out of reach.
An agent that can read the real rows stops guessing about your data. An agent that cannot write to them stops being a risk you have to supervise line by line.
How AgentsRoom reaches a database in a private subnet and answers a read-only query from an AI agent.
An AI coding agent that cannot see your data writes code against the schema it imagined. It invents a column, assumes an enum has three values when it has seven, and explains a bug with a theory instead of a row. Giving it a database connection fixes that, and it is also the fastest way to turn a helpful agent into an incident. AgentsRoom is built around that tension.
You save your connections in the app the way you would in any database client : engine, host, port, user, database, and TLS when the server expects it. If the database is not reachable from the open internet, the connection is routed through an SSH tunnel or an AWS SSM port-forwarding session, using the SSH and SSM connections you already saved in AgentsRoom. That is how a database sitting in a private subnet becomes something you can query without opening it to the world.
Every connection starts read-only. A SELECT runs. A statement that would modify data does not, until you have made that specific connection writable and confirmed the operation. Only one statement is accepted per call, so nothing extra hides behind a semicolon, and result sets are capped so a wide query cannot flood an agent or a window. A connection can also be flagged as production, which makes the confirmation harder to give by accident.
Reading is not the whole job. A connection saved on one machine shows up on your others, so you set a database up once instead of once per computer. And a database can be exported to a file, restored from one, or copied straight onto another server, through the same tunnels: the operations you used to leave the app for.
A Database Client That Assumes an Agent Is Driving
MySQL, PostgreSQL, SQL Server, MongoDB, SQLite and Google BigQuery, the server engines reachable in private networks, with the guardrails on by default.
MySQL, PostgreSQL, SQL Server and MongoDB Connections
Save a connection per database : host, port, user, the database to open and TLS when the server requires it. Your local database, the staging one and the production replica all live in the same list, ready to be picked instead of retyped.
Reach a Private Database
A database in a private subnet is not a special case. Route the connection through an SSH tunnel or an AWS SSM port-forwarding session and AgentsRoom opens it for you, reusing the SSH and SSM connections you already saved in the app. A Google Cloud SQL instance is reached by its connection name through the Cloud SQL Auth Proxy, with your own gcloud login and nothing stored.
Read-Only by Default
A new connection can read and nothing else. Queries return rows, statements that would change data are refused. Nobody has to remember to set the safe mode, because the safe mode is where every connection starts.
Two Locks Before a Write
Writing takes two deliberate acts, not one. The connection has to be made writable, and the operation itself has to be confirmed explicitly. A single careless click cannot chain into an UPDATE without a WHERE clause.
One Statement per Call
Each call carries exactly one statement. Anything stacked behind a semicolon is refused rather than executed, so a read that looks like a read cannot smuggle a second statement along with it. Result sets are capped on top of that.
Production Is Flagged
Mark a connection as production and the confirmation gets harder. The database that matters stops looking exactly like the local copy, both to you at the end of a long day and to an agent working through a task list.
Your Connections, on Every Machine
A connection saved on the office machine is there on the laptop: name, host, port, user, default database and the tunnel it goes through. The password is the one thing that stays behind, encrypted on the machine where you typed it, so each machine asks you for it once.
Export, Import, Copy
Dump a database to a .sql file, replay one into a database, or copy one database straight onto another. The target is backed up before it is overwritten, and replacing it outright is a separate, confirmed decision.
Agents Query the Database, They Never Hold the Password
Your database credentials are stored by AgentsRoom, not handed out. An agent asks to run a query against a connection it knows by name, the app opens the connection, runs the statement and returns the rows. The password is never part of what the agent receives, never part of the query it writes, and never part of the conversation it keeps.
The read-only rule is the second half of that, and for an agent it is not something it could talk its way out of. The tool an agent queries with refuses anything but a read unless two things are true: the connection is writable, and you turned on Allow agents to write for that connection. The option is off by default, and the check runs in the desktop app rather than in the agent's process. Your own writes in the console still ask for an explicit confirmation, deliberately harder to give when the connection is flagged as production. Once a connection is open to agent writes, they run without that confirmation, so keep the option for a database you would trust the agent with. Everywhere else, the worst outcome of a bad query stays a wrong answer rather than a lost table.
The single-statement rule closes the classic gap. A call that carries one statement cannot be extended with a semicolon and a second one, so a query that reads as harmless in a review cannot do something else at execution time. SQL Server does not need that semicolon, so there a read is a SELECT or a WITH with no write or transaction keyword anywhere in it, and it runs inside a transaction that is always rolled back. Combined with capped result sets, a mistake stays a mistake instead of becoming an export.
Six engines, and we name the ones that are missing
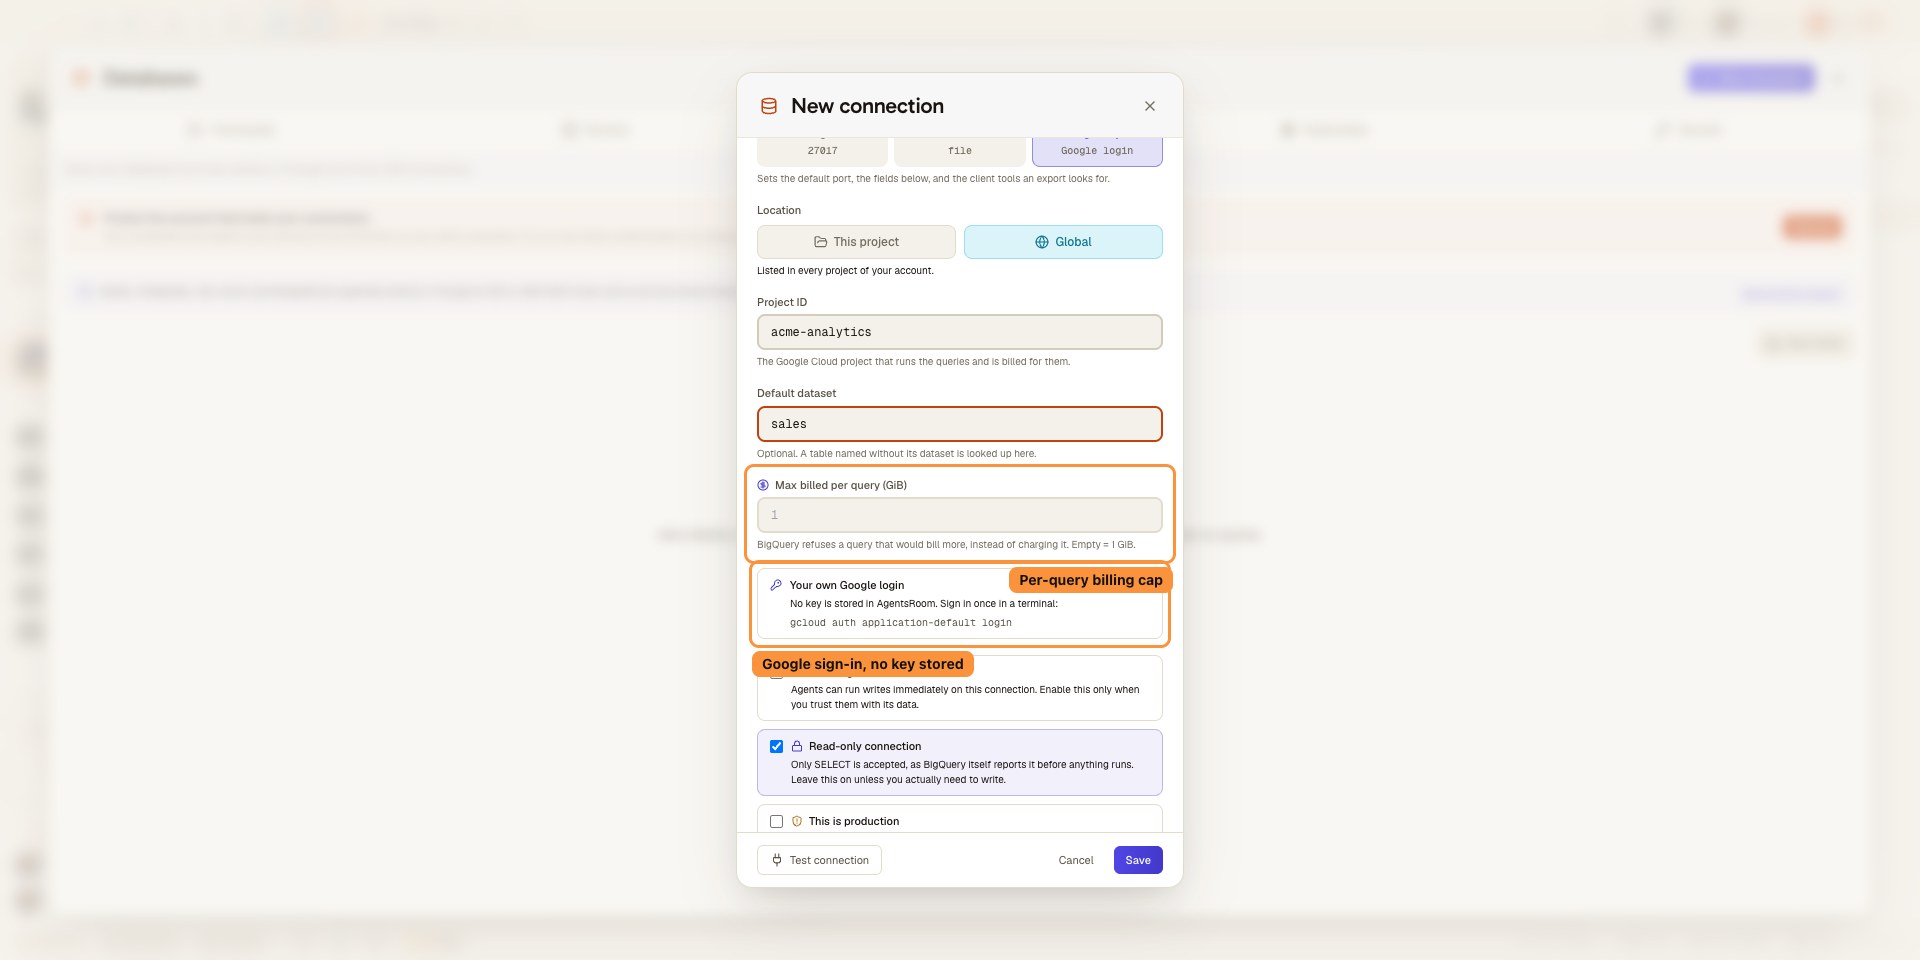
MySQL and MariaDB, PostgreSQL, SQL Server (Azure SQL and Amazon RDS for SQL Server included), MongoDB, SQLite and Google BigQuery. Each one has its own driver rather than a translation layer, because they genuinely differ : a PostgreSQL or SQL Server session binds to a single database, MongoDB takes a query rather than SQL, T-SQL does not need a semicolon between two statements, each export runs the tools that engine ships with, SQLite is simply a file on your computer, with no host, user or password, and a BigQuery connection is a Google Cloud project and a default dataset, signed in with your own Google login (gcloud auth application-default login), with no key stored. The four server engines are reached directly, or through an SSH tunnel or an AWS SSM port-forwarding session when they are not exposed to the open internet.
Oracle, Redis and the others are not supported. On SQL Server, you sign in with a SQL login (Windows, Active Directory and Entra ID authentication are not offered), and there is no export, import or copy. On BigQuery, Google bills every query on the bytes it reads, so each connection has a per-query billing cap (1 GiB by default, adjustable): a query above it is refused instead of charged. Opening a table is free and read-only, your agents use the same db_list, db_schema and db_query tools with the same guardrails and see the bytes each query read, and there is no export, import or copy there either. You deserve to know that before the download rather than after it. Which engine comes next is decided by what people ask for, so if yours is missing, say which one on the public backlog and it gets counted.
Request your database engineMove a database, not just read it
Export a database to a file. Import a file into a database. Or copy one database straight onto another, including through the SSH tunnel or the AWS SSM session you already saved. Each engine runs its own official tools, streamed to disk, so a multi-gigabyte database is a progress bar rather than a crash.
Those tools ship with the database, not with AgentsRoom : mysqldump and mysql, pg_dump and psql, mongodump and mongorestore. SQL Server has no equivalent that streams a whole database, so its connections have no export, import or copy. When the tools are missing, the app says exactly which ones and lets you point at the folder holding them, the way a database client should: launched from the Dock or the Start menu, an app sees a bare PATH and would otherwise claim they are missing on a machine that has them.
Copying is where a wrong click costs a day, so it is built around that rather than around the happy path.
- A read-only connection refuses the import outright, before anything is opened.
- The target is dumped to a file you choose before a single statement is applied.
- The confirmation names the connection and the database, and says louder when the connection is flagged as production.
- Dropping and recreating the target is a separate option, and on a production connection you have to type the database name.
From a Private Database to an Answer
Save the connection, route it, then query it or let an agent do it.
Save the connection
Add the database : host, port, user, the database name, and TLS if the server expects it. Give it a name you will recognise later, and flag it as production if that is what it is.
Route it if it is private
If the database is not reachable directly, point the connection at an SSH tunnel or an AWS SSM port-forwarding session built from the connections already saved in AgentsRoom. A database in a private subnet becomes reachable without exposing it publicly. On Google Cloud, pick the Cloud SQL instance instead: AgentsRoom starts the Cloud SQL Auth Proxy for you.
Query it, or let an agent query it
Run your statement from the app, or let an agent run one over MCP. Read-only until you change it, one statement per call, capped result sets, and an explicit confirmation standing between any write and your data.
When an Agent Needs the Real Rows
The moments where reading production data is the shortest path to the fix.
Debug against real data
The bug only shows for a handful of accounts. Let the agent read those rows and it finds the value that breaks the logic, instead of proposing three theories about what the data might look like.
A database that is not public
The database lives in a private subnet with no public endpoint. Route the connection through an SSH tunnel or an AWS SSM session built on your saved connections, and query it without opening a port to the internet.
Let the agent check, not guess
Before it writes a migration or a query, an agent can look at what is actually stored. It reads, it reports, and unless you opened that connection to agent writes, it has no way to change anything while it does.
Production, without the write risk
Reading production is often necessary, writing to it almost never is in the middle of a task. Flag the connection as production, keep it read-only, and the difference between investigating and breaking stops depending on anyone paying attention.
Refresh staging from real data
The bug only reproduces on real rows. Copy the database onto your staging server, through the tunnel you already saved, with a dump of what was there taken first.
Open the laptop, everything is there
Your connections follow your account: same hosts, same tunnels, same read-only and production flags. With synced passwords on, the passwords follow too, end-to-end encrypted, so nothing is retyped; without it, each machine asks for the password once.
How do my agents query the database?
Through AgentsRoom MCP, with four tools. db_list returns your saved connections and their metadata, db_schema walks the schemas, the tables and the columns without a line of SQL, db_query runs one statement and returns the rows, and db_connection_new proposes a database you have not saved yet. AgentsRoom opens the connection, including the SSH tunnel or the AWS SSM session in front of it when there is one. What travels back to the agent is a result set, never a credential.
Agents can write only when you enable Allow agents to write on a connection that is also writable. This opt-in is off by default and syncs with the connection across your account. Once enabled, writes run immediately, so use it only when you trust the agent with that database. The desktop checks the permission in its main process, and db_query still accepts only one statement per call.
Registering a database can also be entirely the agent's job. db_connection_new keeps the reviewed path: it opens the creation form pre-filled with the host, the user and the SSH or AWS SSM connection it should be reached through, and you review it, type the password and save, nothing being stored until you do. Unless you turn off "Agents can manage connections" (Settings, on by default), db_connection_save writes the connection outright, and the password still never travels through the conversation: it is copied from a vault secret the agent only names. The agent gets what it needs to reason about your data, and none of the ways that access usually turns into an incident are available to it.
Every query an agent runs is visible too. db_query and db_schema calls land in the Activity tab of the right panel, with the SQL and the first rows returned, in one journal per database; the agent's avatar shows on the Databases button and, with an Agent at work badge, in your Databases list. You can also follow it from your phone, in the agent's card of the mobile app. That journal only travels between your computer and your phone, end-to-end encrypted with secrets masked: no result set is stored on a server.
Discover AgentsRoom MCPThe same Activity tab that lists your db_query and db_schema calls, filmed here on a saved SSH server : an agent runs three commands, each one lands with its output, its exit code and its duration, then the journal of that connection opens in full. The journal stays on your computer.
Which databases are supported?
Can an AI agent write to my database?
How do I reach a database in a private subnet?
Do my agents see the database password?
Can an agent run several statements at once?
What does flagging a connection as production change?
What happens with a query that returns a lot of rows?
Can an agent add a database connection?
How does an agent learn my schema?
Are my database connections synced between my machines?
Can I dump a database and import it somewhere else?
How is the account that holds my connections protected?
Screenshots
Real captures of the app, added as this feature evolves.
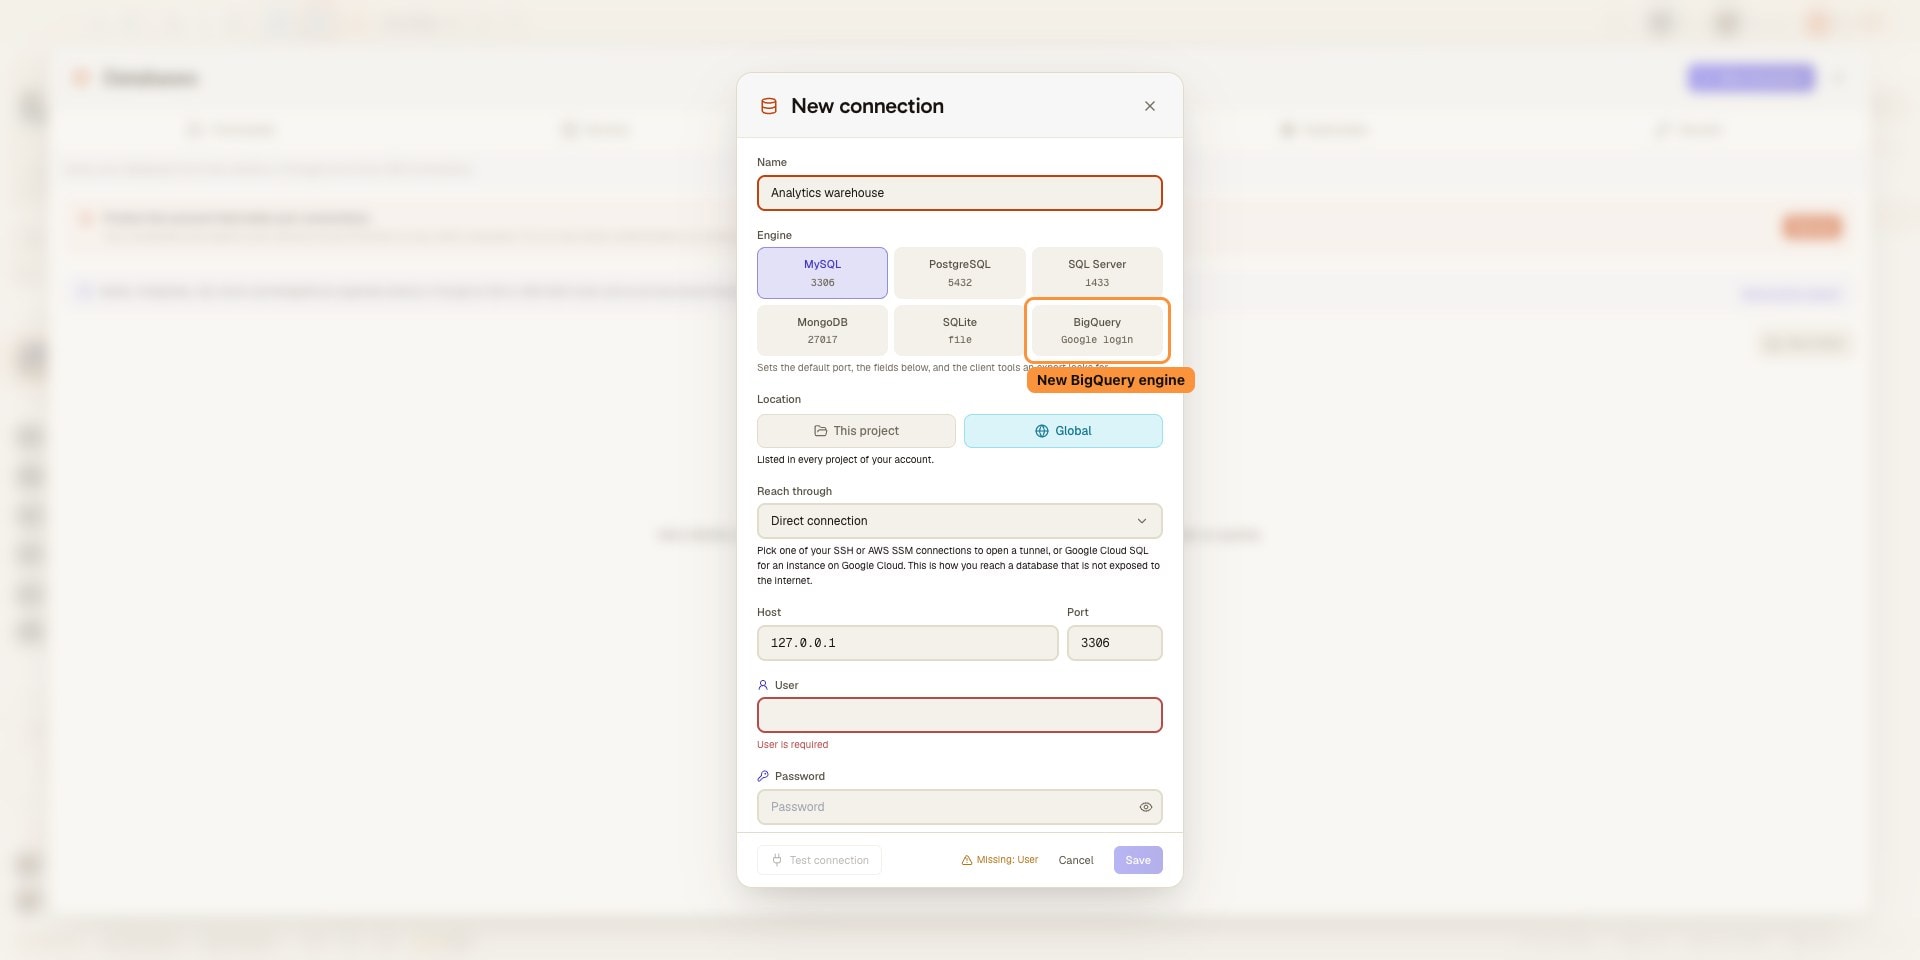
Connect Google BigQuery with your own Google login 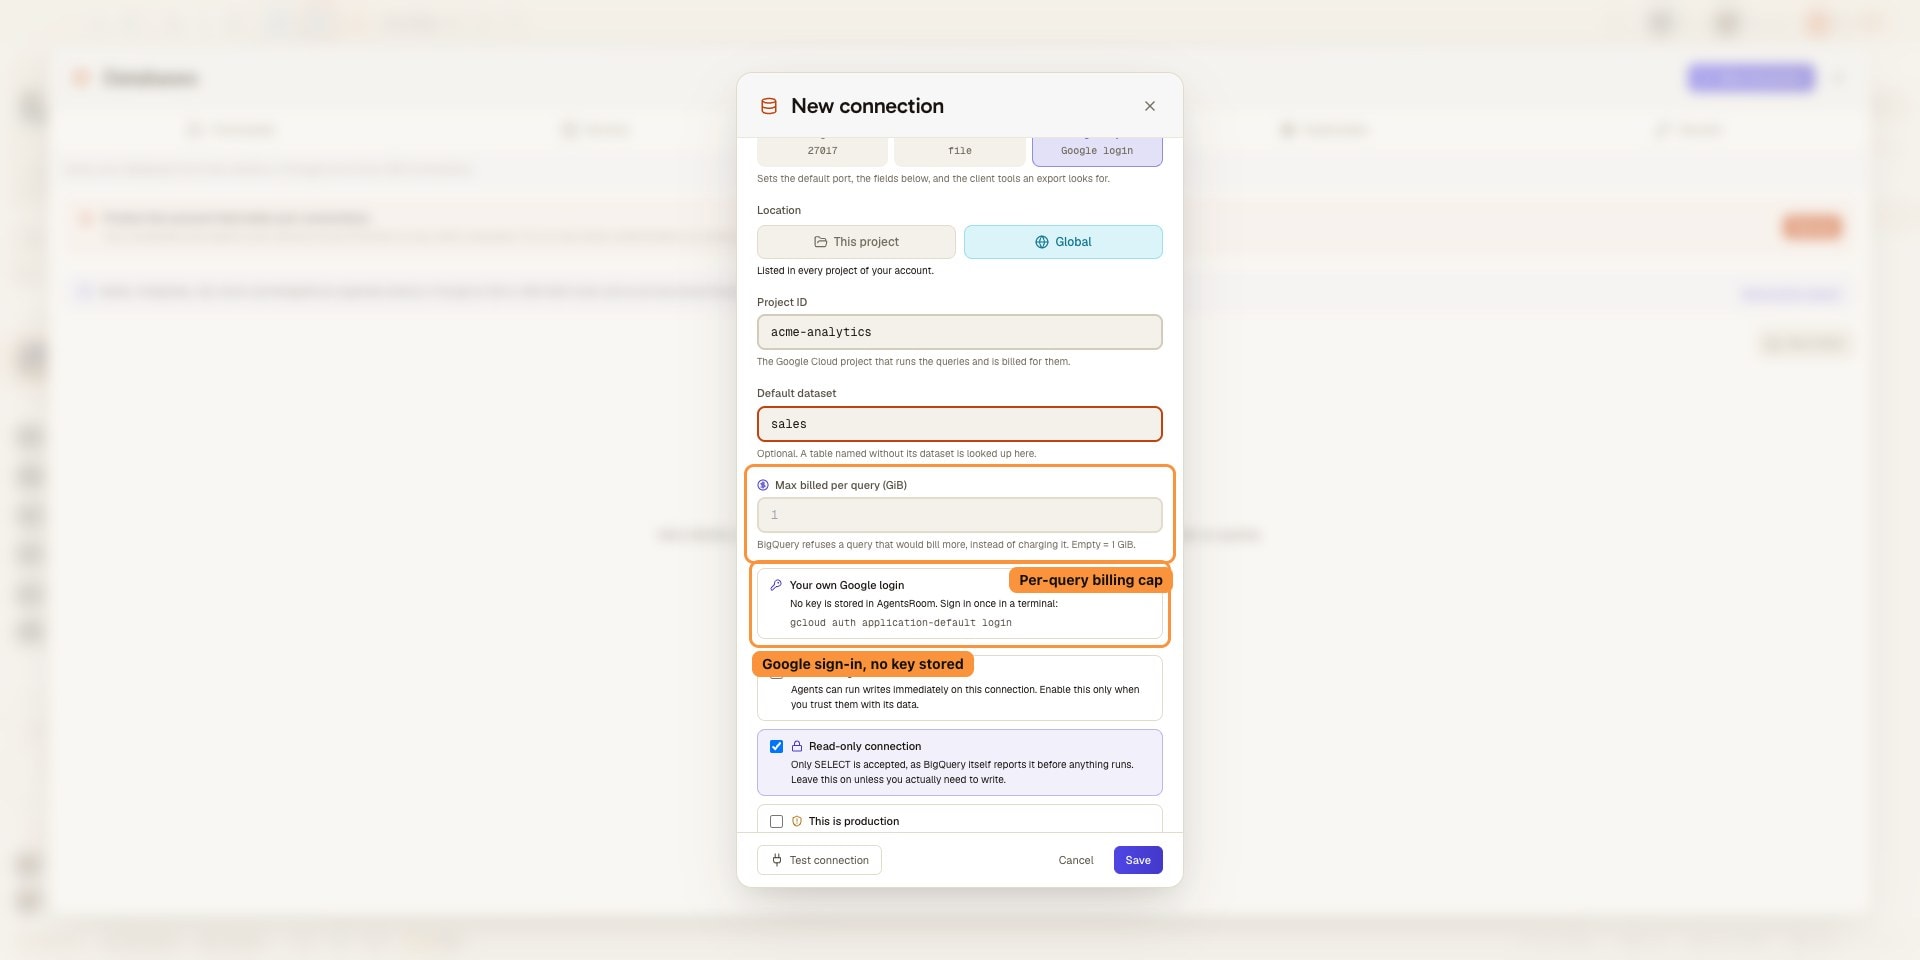
Cap what one BigQuery query may bill, per connection 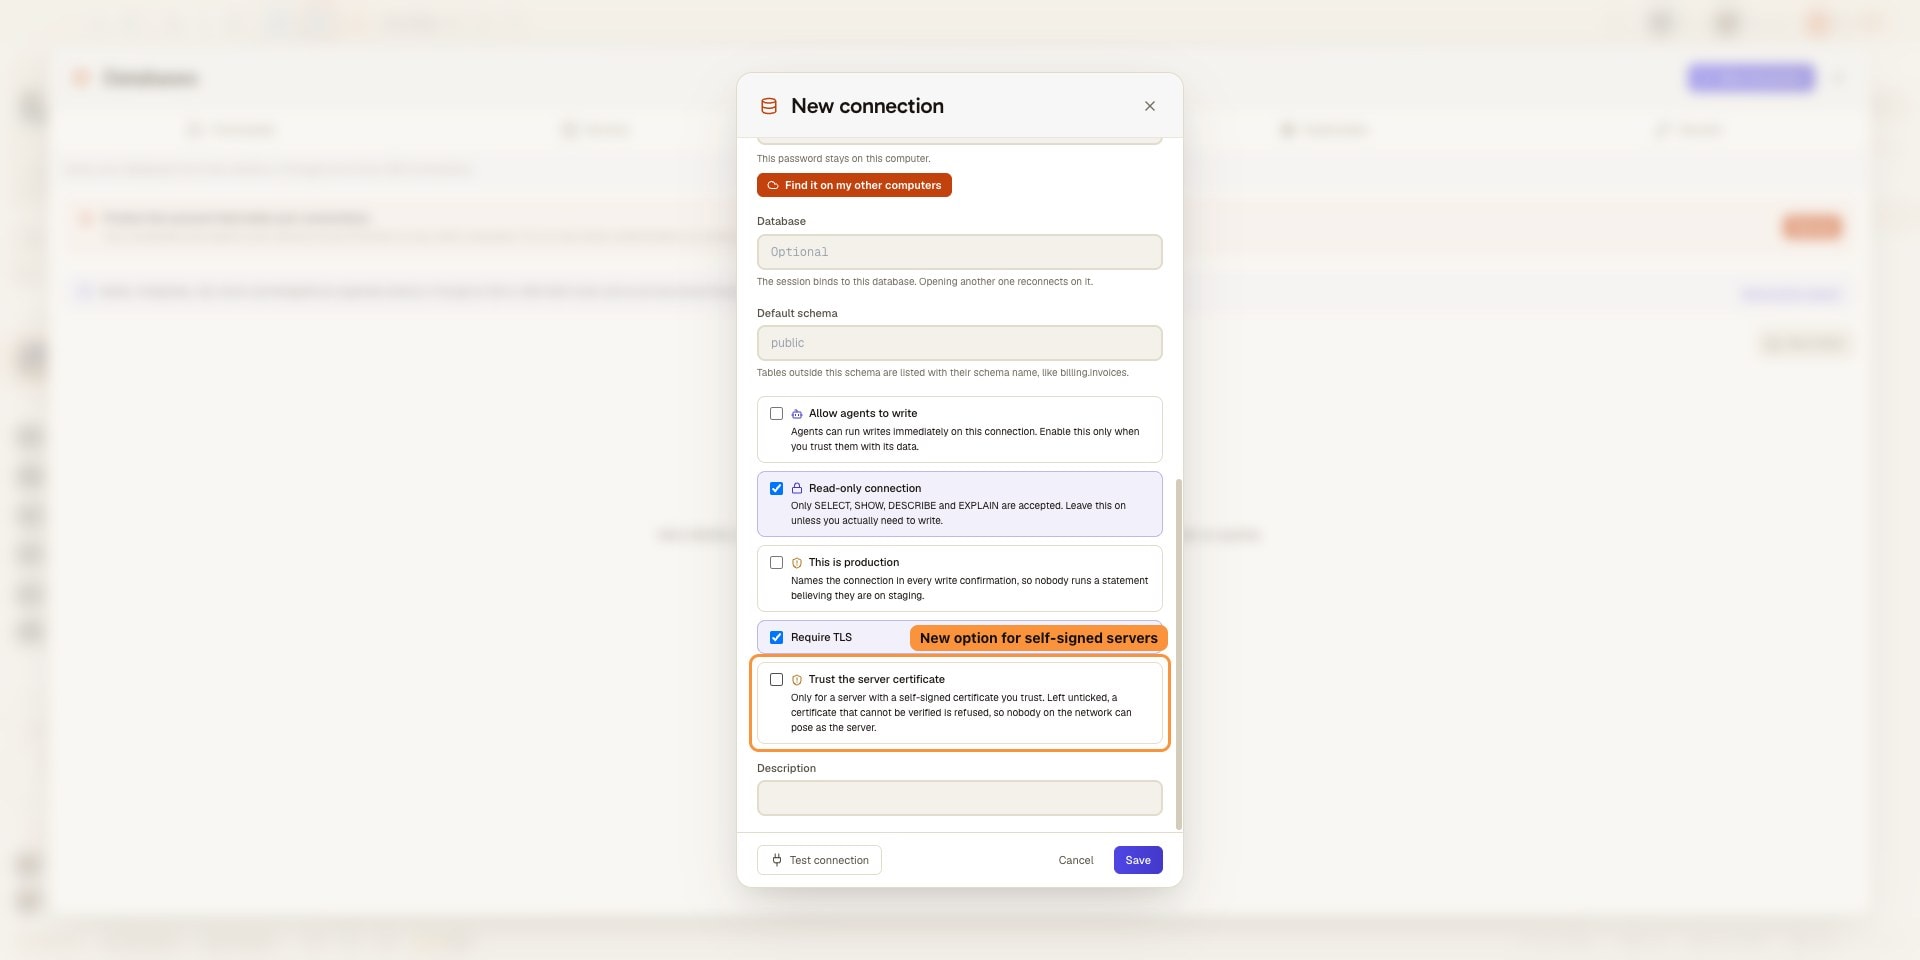
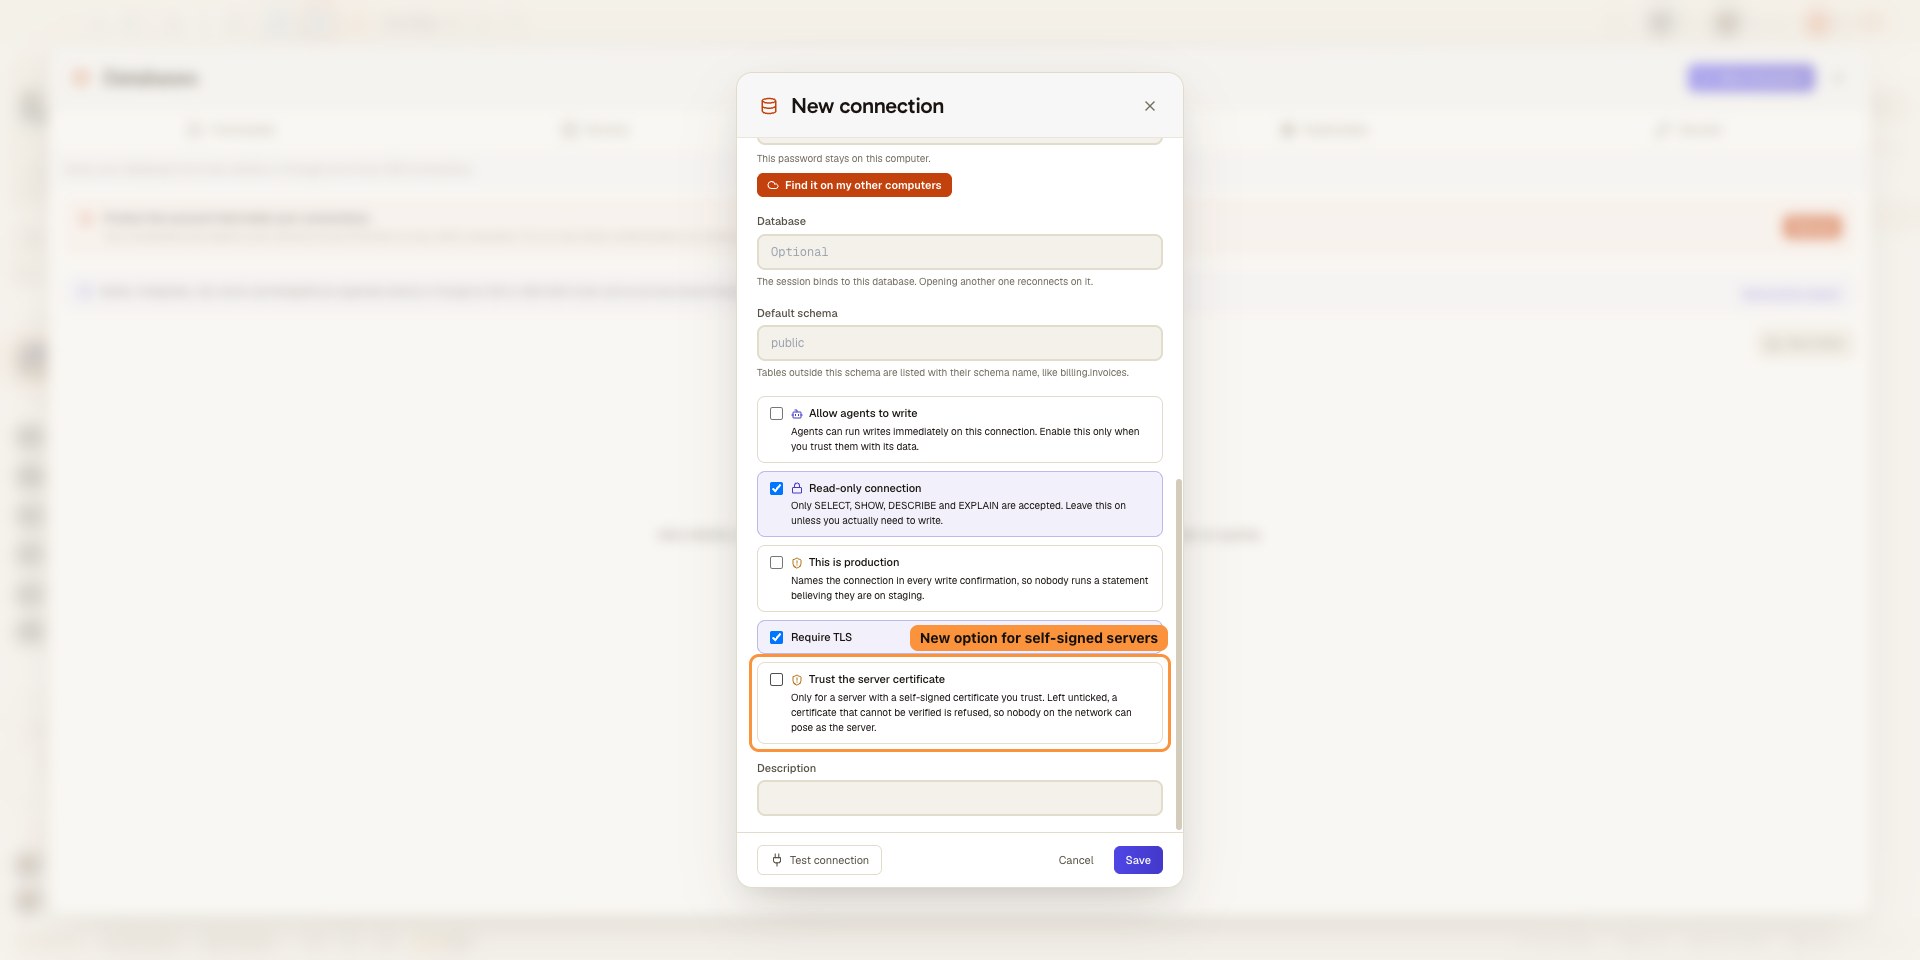
Direct TLS connections verify the server certificate, with an opt-in for self-signed servers
You may also like
RDS through AWS SSM
Reach an Amazon RDS instance that has no public endpoint, from your own machine, through aws ssm start-session and the AWS-StartPortForwardingSessionToRemoteHost document. No bastion to maintain, no VPN, no inbound SSH rule. AgentsRoom opens the session on a loopback port and connects its database client through it. MySQL, PostgreSQL, SQL Server and MongoDB, so RDS MySQL, RDS PostgreSQL, RDS for SQL Server, Aurora and DocumentDB.
Cloud SQL Auth Proxy
Reach a Cloud SQL for MySQL or PostgreSQL instance from your own machine, private IP included, without a bastion VM. AgentsRoom starts the Cloud SQL Auth Proxy on a loopback port with your gcloud Application Default Credentials, supports IAM database authentication, and lets AI agents query it read-only.
SSH Connections
Save your SSH connections, open a built-in terminal over SSH, and run Claude Code, Codex or Antigravity CLI directly on your remote server or VPS. SSH key or password auth, per-project connection profiles, no separate SSH client needed.
Secret Manager
Store API keys, tokens and passwords in your OS keychain, reference them as {{secret:NAME}} in dev commands and agent environments, and let AgentsRoom resolve them at launch. Agents see the names, never the values, and nothing is ever synced to a server.
Dev Terminals
Per-project terminal manager and process launcher. Start backend, frontend and workers in one click, locally or on a remote server.
AgentsRoom MCP
The MCP server that lets your agents drive AgentsRoom itself : projects, terminals, backlog and connections, with the guardrails that come with it.
































Give Your Agents the Data, Not the Keys
Download AgentsRoom, save your MySQL, PostgreSQL, SQL Server, MongoDB, SQLite and Google BigQuery connections, reach the server ones through an SSH tunnel or an AWS SSM session, and let your agents query them, read-only unless you open a connection to their writes.
Companion app: monitor your agents on the go
Bring your own: Claude, Codex, Antigravity CLI, or other AI provider.
Push bugs and requests straight to your public backlog.
Agents you read like a conversation
Each agent has a role, a face, and a thread you read like a messaging app.
